FLASHPOINT IGNITE » VULNERABILITY INTELLIGENCE
Flashpoint Vulnerability Intelligence
Flashpoint Vulnerability Intelligence fuses NVD-independent data, real-time exploit analysis, non-CVE visibility, and advanced scoring. Get the speed and insight required to prioritize effectively and diminish the attacker’s advantage.
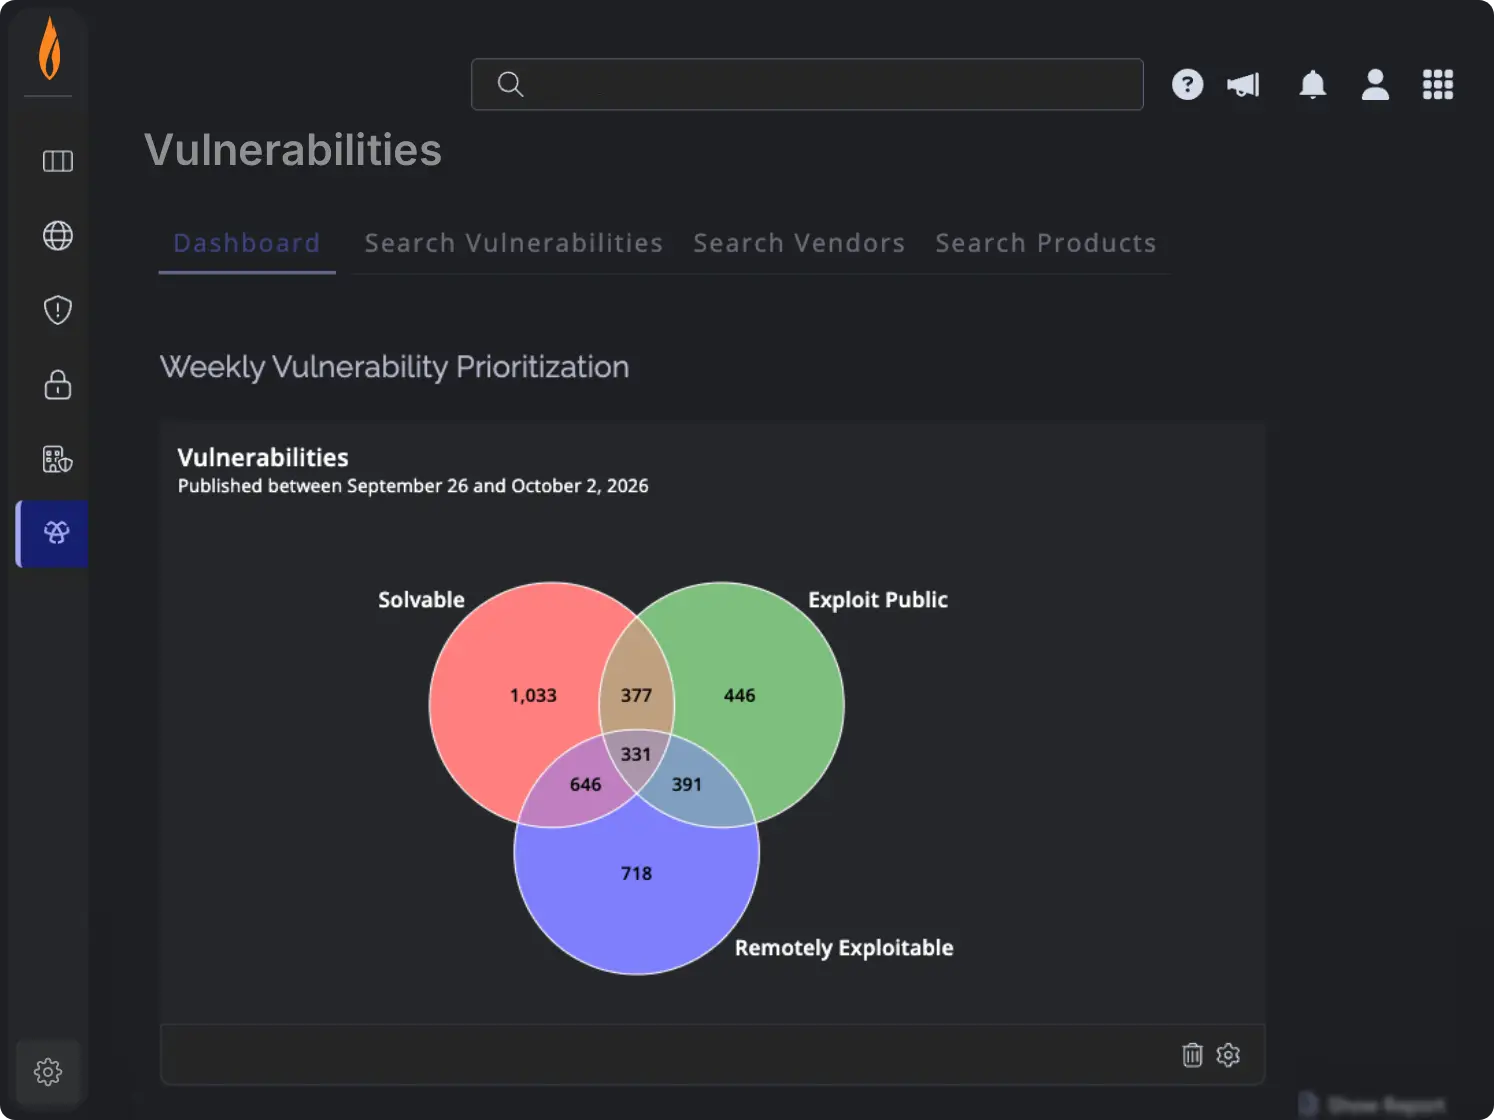
How Teams Use Flashpoint Vulnerability Intelligence

Intelligence-Led Prioritization
Threat analysts can correlate vulnerability exposure with threat activity and attacker TTPs to pinpoint the highest-risk vulnerabilities.

Seamless Workflow Integration
Vulnerability analysts can deploy vulnerability intelligence with robust integrations and partnerships to ensure quick time to value.

Proactive Software Supply Chain Security
DevSecOps and AppSec teams can support their organizations supply chain security with visibility into affected components, open-source libraries, and dependencies using formats like SBOM.

Strategic Risk Alignment & Reporting
Vulnerability, threat, and exposure analysts can translate vulnerability exposure into clear executive-level reporting and drive informed investment decisions.
What Flashpoint’s Vulnerability Intelligence Delivers
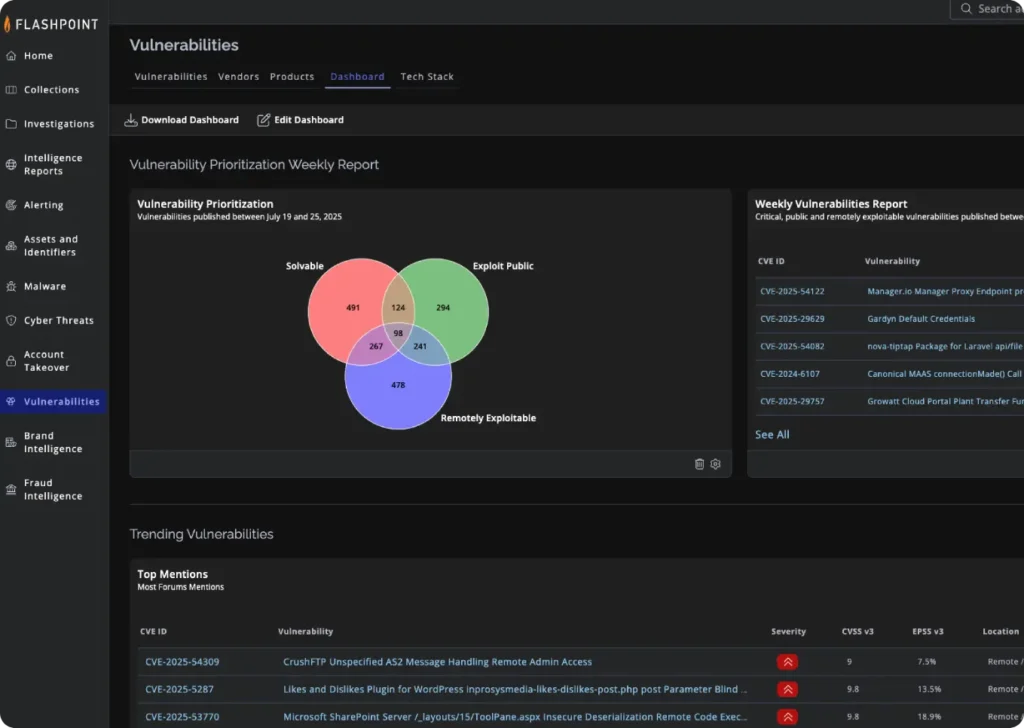
Uncover Critical Flaws Missed By Public Sources
Eliminate dangerous blind spots across your organization with intelligence built on over 415,000 vulnerabilities and rapid time from disclosure to publication (on average 2 weeks faster than NVD). By continuously staying on top of the vulnerability landscape, we deliver comprehensive visibility on vulnerabilities whether they have a CVE ID or don’t.
Does Flashpoint Vulnerability Intelligence include vulnerabilities that are not yet assigned a CVE ID?
Yes, our database includes all CVEs, including 105,000+ not found in NVD and 800+ known exploited vulnerabilities without CVE IDs, ensuring you have full visibility into critical flaws often missed by public sources.
How does Flashpoint’s vulnerability database compare to Vulncheck?
VulnDB delivers threat-informed visibility up to three weeks faster than NVD-based tools, tracking 700+ non-CVE and exploited-in-the-wild vulnerabilities, hidden flaws, zero-days, and active exploits. Read more
Prioritize Risk with Real-Time Exploit Context
Move faster than the adversary. We fuse exploit intelligence, including Ransomware Likelihood and Social Risk Scores, directly into your triage process. This allows you to focus remediation efforts on the critical risks that are actively being exploited, accelerating response time.
How much faster is Flashpoint’s intelligence feed than relying solely on the NVD?
Our intelligence is often available days to weeks faster than the NVD. This speed is critical because attackers operate on an hourly, not daily, timeline.


Anticipate Attacks with Threat-Informed Context
Unify your CTI, VM, and AppSec teams around a single, trusted source of truth. We go beyond basic scoring, providing MITRE ATT&CK mapping, exclusive FP KEV tagging and much more, to ensure every customer of Flashpoint Vulnerability Intelligence operates with actionable context and a strategic advantage.
How does Flashpoint support my organization’s move toward CTEM?
We provide the crucial vulnerability and threat context needed for the prioritization and validation phases of Continuous Threat Exposure Management (CTEM).
How much context do you provide for each vulnerability?
We deliver ~60+ rich data points per vulnerability, including exploit maturity, threat actor chatter, and FP KEV status, to help drive action and triage. This enables lightning-fast detection rule generation and risk-based decision-making.
Analyst Support
Instantly expand your security skillsets by submitting Requests for Information (RFIs) directly within the platform to access Flashpoint’s world-class intelligence experts. This alleviates strain on internal resources and delivers tailored, deep-dive reports when critical threats emerge.
Is expert analyst support included with Flashpoint?
Absolutely. Direct access to Flashpoint’s analyst team for RFI’s is a core feature in the Vulnerability Intelligence offering, maximizing your team’s effectiveness.

Additional Offerings to Pair with Vulnerability Threat Intelligence
Cyber Threat Intelligence (CTI)
Intelligence links vulnerabilities to broader threat data like TTPs for strategic context and decision-making. Provides adversary profiles and dark web intelligence to enrich vulnerability context and anticipate attack paths.

External Attack Surface Management
EASM continuously discovers your internet-facing assets, including domains, subdomains, and IPs, and connects them to Flashpoint Vulnerability Intelligence. Receive alerts when new assets are discovered and when new vulnerabilities are detected on your perimeter.

Integrations & APIs
Integrated intelligence drives action, delivering better workflows through robust API access. Enhances security outcomes by enabling automated data exchange with existing tools for quick time to value and reduced manual effort.
Flashpoint Vulnerability Intelligence FAQs
-
We gather data from thousands of vulnerability disclosure sources, including illicit communities, private forums, vendor advisories, and security research that bypass the official CVE/NVD process. This scope, far exceeding the hundreds used by many competitors, enables us to cover over 100,000 vulnerabilities the public source misses.
-
VulnDB® was acquired by Flashpoint in 2022. The VulnDB dataset is now available in Flashpoint Vulnerability Intelligence.
-
Our intelligence is consistently available days to weeks faster than the NVD. This speed is critical because attackers often weaponize vulnerabilities in less than 24 hours after public disclosure, giving you the time needed to act.
-
We support CTEM by providing the critical threat and asset context needed for the Prioritization and Validation phases, helping security teams continuously identify and focus on the exposures most likely to be exploited.
-
A scanner identifies if a vulnerability exists on your network; our intelligence tells you how critical that vulnerability is based on external threat actor activity and exploit availability. This intelligence, often paired with human-led analysis and technical notes, provides the context needed for confident prioritization.
-
We prioritize by fusing basic severity scores with advanced contextual metrics, including exploit availability, threat actor chatter, and our proprietary Ransomware Likelihood score. This includes human-led vulnerability analysis and notes to ensure true risk alignment.
-
Yes, our coverage is comprehensive, extending beyond primary applications to include critical vulnerabilities found in third-party libraries, open-source components, and the software supply chain.
-
Yes, our intelligence includes monitoring deep and dark web forums to provide context on threat actor intent, motivations, and the vulnerabilities they are actively discussing or selling access to.
-
Yes, our robust API and native integrations are designed to flow data seamlessly into your existing security stack (SIEM, SOAR, CMDB) for automated triage and response.
-
Flashpoint supports DevSecOps by providing actionable intelligence and SBOM-based vulnerability mapping, enabling developers to identify and remediate flaws in open-source components during the build phase.
-
Flashpoint Ignite enables SOCs to unlock vulnerability intelligence and dark web monitoring capabilities. With over 3.6 petabytes of data from across the deep and dark web, plus 6000+ KEVs, Flashpoint’s depth of intelligence is industry best.
Product News
-
Aug 6: Search and Discover Using Natural Language in Echosec
Flashpoint’s geospatial open-source intelligence tool, Echosec, now features Natural Language Search and AI Results Refinement, bringing an intuitive approach to search and discovery in the Locate view.
-
 Product Updates
June 25: Introducing the Flashpoint MCP Server
Announcing a major transformation for Flashpoint Managed Attribution: a full product redesign and the introduction of the powerful, built-in Anonymous Browser capability.
-
Product Updates
May 28: Intelligence Requirements in Flashpoint Ignite
Announcing a major transformation for Flashpoint Managed Attribution: a full product redesign and the introduction of the powerful, built-in Anonymous Browser capability.
