CYBER THREAT SOLUTIONS » NATIONAL SECURITY INTELLIGENCE
Flashpoint for
National Security
Flashpoint National Security Solutions (FNSS) provides industry-leading Open-Source Intelligence (OSINT) solutions, investigative support, and finished intelligence empowering defense, law enforcement, and government agencies to inform, operate, defend, and influence.
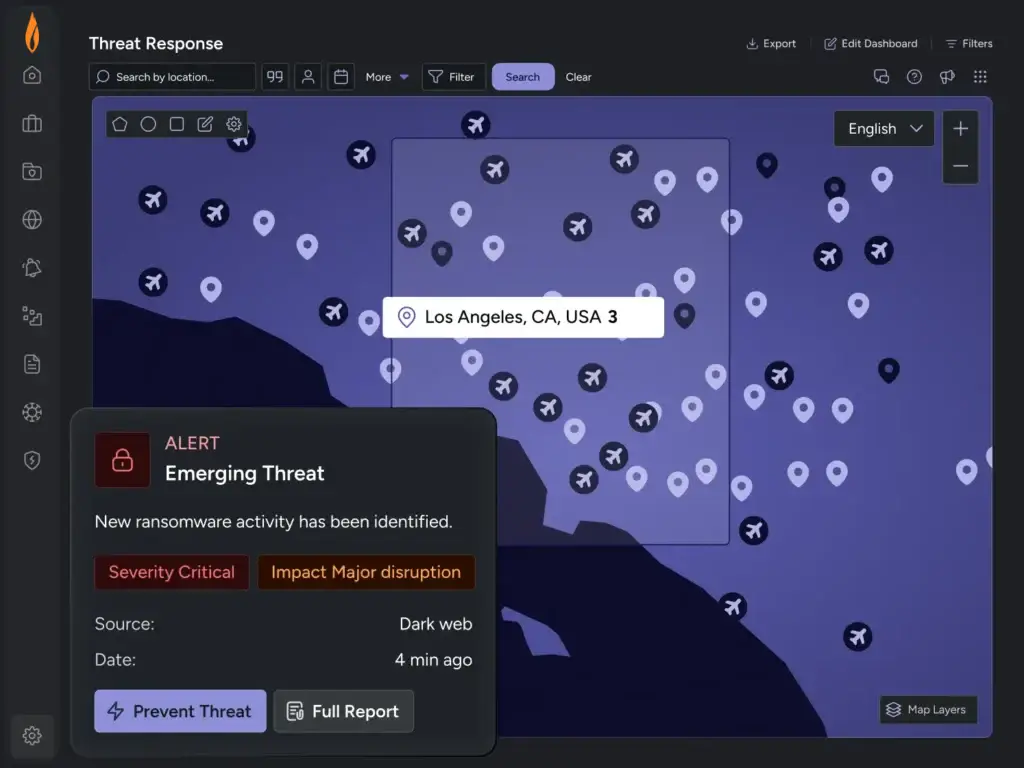
Tools Aligned to Your Critical Mission
Unlock the world’s open and difficult-to-reach digital spaces, from mainstream social media, to chat services, and dark web communities, and access critical tools to analyze the data to generate actionable intelligence. Flashpoint’s dual-use solutions are purpose-built to support the unique requirements of our government partners:

Defense
Gather tailored data and timely intelligence for integrated deterrence, defense intelligence, cyberspace operations, and force protection.

Law Enforcement
Accelerate Investigations. Identify criminal activity, organizations, and threat actors across the deep and dark web to enhance public safety.

Intelligence Community
Reduce intelligence gaps with Flashpoint’s proprietary, asymmetric data collections. Flashpoint supports all phases of the intelligence cycle.

Public Sector
Monitor illicit open, deep, and dark web communities to protect sensitive government data, infrastructure, and maintain real-time situational awareness against emerging cyber and physical threats.
Mission Threats & Use Cases
Flashpoint serves as an extension to your team and includes experts from retail, financial services, law enforcement, government, and more. Our team has deep experience working in mission-critical government roles. We understand the challenges you face, we speak your language, and we are committed to being your trusted partner.
All of Flashpoint’s activities are aligned with U.S. laws, reflect the guidance of law enforcement, and are compliant with US Department of Justice guidelines on data collection from illicit sources. Flashpoint is also GDPR, CCPA, and EU Privacy Shield compliant.
Defense
Threat Indications and Warning: Planning Through Dissemination
Access to specialized data feeds and raw data consumption (APIs) for ingestion into existing intelligence systems, enabling the timely correlation of foreign cyber activity and strategic warning indicators.
Operational/Physical Security: Force Protection/Cyber
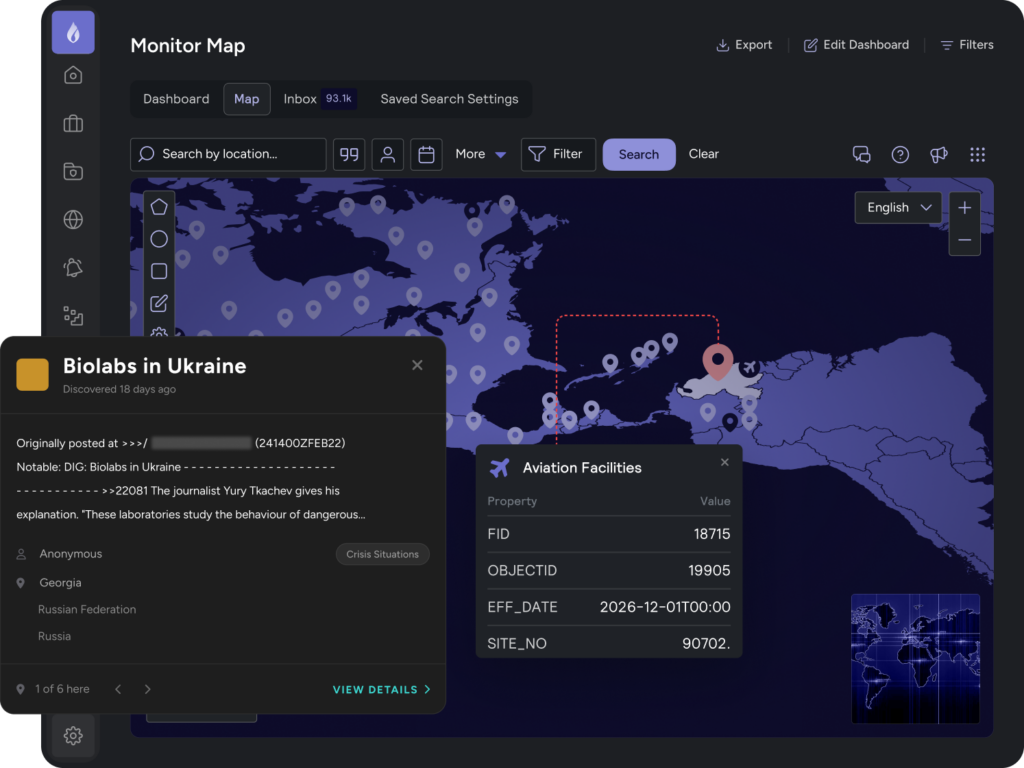
Real-time, localized intelligence from multiple source streams (e.g. chat services and social media) to identify and monitor current threats to assets, infrastructure, and deployed personnel, including insider threats and extremist mobilization.
Foreign Malign Influence and Information Operations (IO)
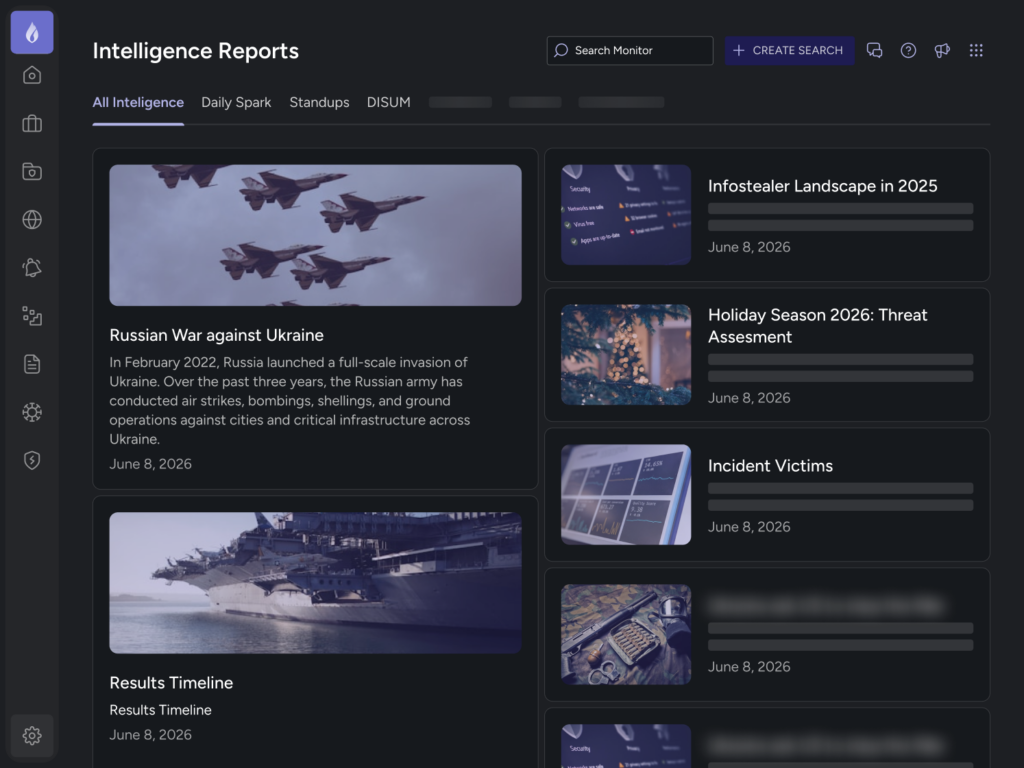
Deep access to online communication (foreign-language forums, fringe communities, and state-controlled platforms) to detect and analyze narrative campaigns, understand sentiment and assess intent.
Law Enforcement
Complex Investigations & Attribution
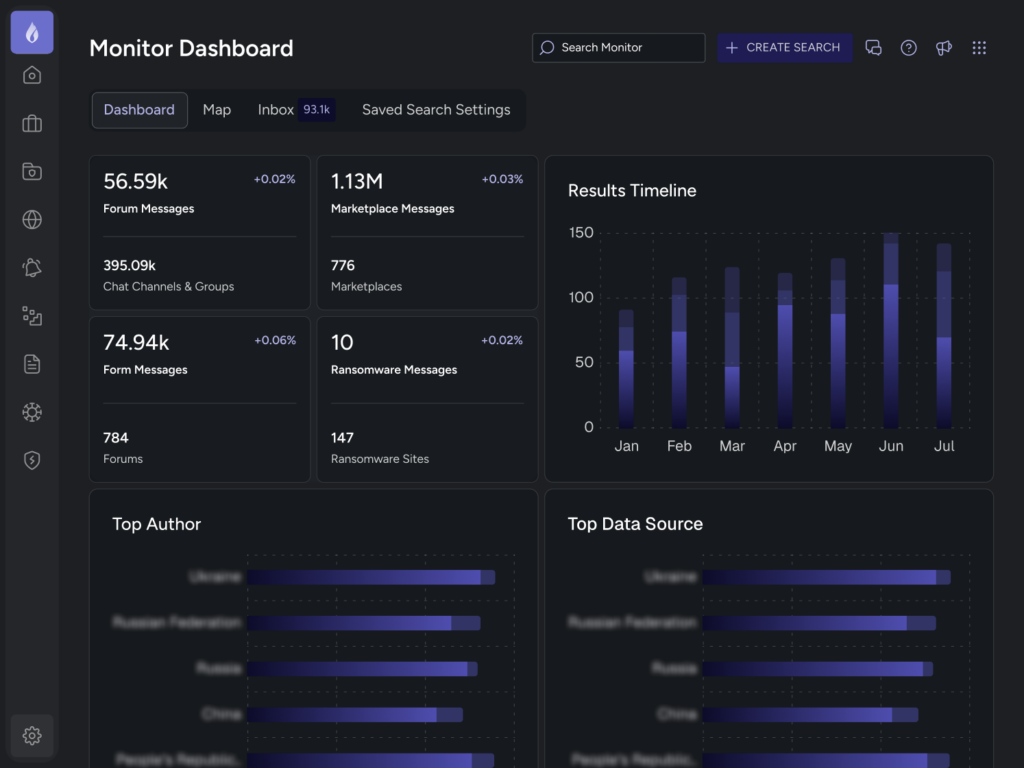
Unrivaled primary source data from deep and dark web marketplaces, closed chat groups, and specialized collections to map criminal networks, identify malicious actors, and gather critical evidence.
Public Safety & Real-Time Threat Monitoring
Real-time geospatial OSINT to proactively monitor for physical threats to critical infrastructure, events, or specific individuals, for informed event planning and rapid response to emergent threats.
Nihilistic Violent Extremism (NVE) or Violent Online Networks (VONs) Insights & Identification
Actionable intelligence to counter threats from decentralized, highly dangerous, international groups and individuals, protecting vulnerable persons and the community at large.
Intelligence Community
PAI and CAI Data Collection
Delivering asymmetric datasets to fill critical intelligence gaps where traditional collection methods are not viable or available. Providing the source of the information and in most cases raw data to analysts, key principals, and decisions makers.
Secure Virtual Operations
Providing analysts with secure virtual environments to safely explore and interact with unique information within threat actor communities on the deep and dark web without compromising identity, infrastructure, or source fidelity.
Threat Actor Infrastructure & Selector Enrichment
Correlating identity information, forum activity, and technical indicators across disparate online communities to build high-confidence profiles for mission-critical targeting and collection planning efforts.
Public Sector
Proactively Defend Networks and Infrastructure
Identify and mitigate vulnerabilities before they impact your organization. Gather threat actor information to proactively stay ahead of criminal activity and cyber threats impacting your digital infrastructure.
Prevent Financial Loss and Account Compromise
Detect fraud indicators across the cybercriminal economy to prevent monetary loss. Flashpoint Account Takeover identifies compromised enterprise and customer accounts to stop the exploitation of confidential information.
Enhance Physical Security and Situational Awareness
Improve situational awareness with near-real-time global social media data. Stay ahead of online chatter threatening public spaces, such as school safety or election facilities, and critical nearby events.